• Our new ticketing site is now live! Using either this or the original site (both powered by TrainSplit) helps support the running of the forum with every ticket purchase! Find out more and ask any questions/give us feedback in this thread!

BBC News: Hackers could delay trains

Status
Not open for further replies.

northwichcat

Veteran Member
Joined
23 Jan 2009
Messages
32,692
Location
Northwich
A shift to a mobile communications technology could expose rail networks to hackers, according to a security expert.

Prof Stefan Katzenbeisser made the claim at the Chaos Communication Congress in Berlin.

The professor said that the systems which switch trains from one line to another could be shut down if encryption keys went astray.

He stressed that trains would not be danger, but there could be delays.

Train-switching systems have historically been controlled by proprietary analogue systems.

At the end of the last century, more than 35 incompatible systems were used for railway communications across Europe.

Prof Katzenbeisser believes the system is relatively secure from hackers under normal circumstances. However, the computer science expert from Technische Universitat Darmstadt warns that encryption keys, used to protect the communications, could pose risks.

"The main problem I see is a process of changing... keys. This will be a big issue in the future, how to manages these keys safely," he told Reuters news agency at the conference.

The news agency said the keys are downloaded to physical media such as USB sticks before being distributed for installation.

It said the risk would occur if one of them fell into the wrong hands. This could allow hackers to mount a denial of service attack by overwhelming the signals system with traffic, forcing it to shut down.

"Trains could not crash, but services could be disrupted for some time," the professor said.

http://www.bbc.co.uk/news/technology-16347248
 
Sponsor Post - registered members do not see these adverts; click here to register, or click here to log in
R

RailUK Forums

jopsuk

Veteran Member
Joined
13 May 2008
Messages
12,774
"if something reasonably unlikely happens, disruption but no danger will happen".

Not going to be losing sleep over this...
 

amcluesent

Member
Joined
19 Dec 2010
Messages
877
All the kit will have been sourced in China, so they'll have added some 'features" and could take remote control of our railways from Bejing easy as pie.
 

ralphchadkirk

Established Member
Joined
20 Oct 2008
Messages
5,754
Location
Essex
All the kit will have been sourced in China, so they'll have added some 'features" and could take remote control of our railways from Bejing easy as pie.

:lol: I don't thing I've ever read something so ridiculous since I've been on this forum!
 

ANorthernGuard

Established Member
Joined
8 Oct 2010
Messages
2,662
"if something reasonably unlikely happens, disruption but no danger will happen".

Not going to be losing sleep over this...
I would like to apogise for the delay to this service, this is due to hackers

Suddenly you hear the sound of 100 laptops slamming shut :)
 

amcluesent

Member
Joined
19 Dec 2010
Messages
877
I don't thing I've ever read something so ridiculous since I've been on this forum

It's not a laughing matter! Much of our national infrastructure contains Chinese made electronics that can 'call home' using the t'interweb. By contracting with the lowest bidder, the public sector has been installing counterfeit and modded gear for years, no-one knows just what kit already, is or could be, controlled by the PRC.

Report Details China's Electronic Espionage Apparatus
 
Last edited:

Jock

Member
Joined
15 Jul 2011
Messages
60
Location
Auchtermuchty
All the kit will have been sourced in China, so they'll have added some 'features" and could take remote control of our railways from Bejing easy as pie.

In the time I've been browsing this forum I too, have never seen such a ridiculous post untill now.


ralphchadkirk

Established Member
Joined
20 Oct 2008
Messages
5,754
Location
Essex
It's not a laughing matter! Much of our national infrastructure contains Chinese made electronics that can 'call home' using the t'interweb. By contracting with the lowest bidder, the public sector has been installing counterfeit and modded gear for years, no-one knows just what kit already, is or could be, controlled by the PRC.

Report Details China's Electronic Espionage Apparatus

You believe all that? Do you think that the military and safety critical industries will just blindly accept electronics without thoroughly checking and testing them?

I hope your tin hat is comfortable.
 

tsr

Established Member
Joined
15 Nov 2011
Messages
7,400
Location
Between the parallel lines
I don't believe that the country is at risk from the manufacturers of the equipment that the government has acquired, at least not in circumstances that we know about, but it is absolutely right to be concerned about the security of encryption and certification keys. At the moment, they are not handled correctly, given the disruptive potential they could have.

It's a bit like storing your credit cards in your back pocket. One day, a pickpocket will steal them. The worrying thing is you don't know when and you most certainly don't know how the criminal is going to use them.

Oh, and one last thing: a hacker who turns criminal is normally called a cracker. For example, I'm a hacker, but I don't ever use my skills for criminal purposes - just for checking network security with full permission from owners.
 

HSTEd

Veteran Member
Joined
14 Jul 2011
Messages
20,326
And why on earth are these systems connected to the internet in the first place, shouldnt the railway have its own communications net.... I do believe it has the rights of way to manage that.
 

Sacro

Member
Joined
20 Jan 2010
Messages
383
The professor said that the systems which switch trains from one line to another could be shut down if encryption keys went astray.

As could many other systems (see HDCP, HD-DVD encryption, PS3 for what not to do).

The trick is to

a) Not let the encryption keys go astray
b) Have a quick and easy process for revoking/reissuing keys.
 

68000

Member
Joined
27 Jan 2008
Messages
832
I am struggling to follow this, GSM-R rollout is secure voice communication between signaller to/from driver.

GSM-R will not be used to send commands to switch points. It is used as a data radio for sending movement authority from ETCS.
 

Schnellzug

Established Member
Joined
22 Aug 2011
Messages
2,926
Location
Evercreech Junction
i suppose it must be real, but Prof Stefan Katzenbeisser does sound rather like a made up name, doesn't it. The Chaos Communication Congress in Berlin sounds like it might be fun, though.

Anyway, how could you hack into links from signalling centres to points & signals? I don't understand much about technology, but it seems a little far-fetched to me.
 

185

On Moderation
Joined
29 Aug 2010
Messages
5,709
Cool. Grand theft auto online hooked up to Piccadilly's main panel?

Wouldn't make much difference to be fair.
 

michael769

Established Member
Joined
9 Oct 2005
Messages
2,008
"This article has been sponsored by FUD Security, buy your copies of FUD anti-virus for Class 170s and FUD Intrusion Detection for Class 380s now!"
 

Tim R-T-C

Established Member
Joined
23 May 2011
Messages
2,143
This is becoming a rather common news story, same has been said for various American public services too (rumours that hackers destroyed a rural pumping station in the US with a DoS attack proved to be false).

You believe all that? Do you think that the military and safety critical industries will just blindly accept electronics without thoroughly checking and testing them?

Actually, you would be surprised how little checking is done. I used to work for a software company and we supplied business mapping software to several government departments and there was never any attempt to check the code. The software itself reported the computer's IP and MAC addresses when the user registered IIRC. While perhaps the idea of a major government sponsoring such espionage is unlikely, it would not be hard for a programmer to include the relevant code into software and allow a user to record keystrokes for example.
 

NSEFAN

Established Member
Joined
17 Jun 2007
Messages
3,518
Location
Southampton
Anything to do with rail signalling has to be failsafe. My understanding is that the interlocking is still fundamentally electronic, so even if you were to remotely try and cause two trains to crash by compromising a control centre, the interlocking wouldn't let it happen.

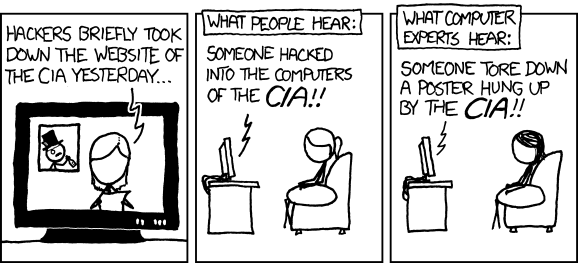
Another scaremongering story. Time for some XKCD:

cia.png
 

Tracky

Member
Joined
18 Jul 2011
Messages
483
I believe that hacking will become a much bigger problem generally over the coming years.

I do believe that the railway is/will be exposed to some risk. It may all be failsafe, and so the worst that can be done is to stop trains but if that happened for an extended period of time it would cause problems. Lets face it, if people are stuck on a train for an hour they get angry, and for any more than that they start breaking out.

With signallers controling greater areas the ability to talk drivers past signals is reduced so whatever the cause of signal failures, it is a problem that few seem to be facing up to.

I read somewhere that in the event of a total failure of one signalling centre, others will be able to take control of bits of its area. Part of me prefers the idea of bits of wood bolted to posts and tied to a lever in a box with a man who waves with a cheerful smile... or not...
 

tsr

Established Member
Joined
15 Nov 2011
Messages
7,400
Location
Between the parallel lines
I believe that hacking will become a much bigger problem generally over the coming years.

I do believe that the railway is/will be exposed to some risk. It may all be failsafe, and so the worst that can be done is to stop trains but if that happened for an extended period of time it would cause problems. Lets face it, if people are stuck on a train for an hour they get angry, and for any more than that they start breaking out.

With signallers controling greater areas the ability to talk drivers past signals is reduced so whatever the cause of signal failures, it is a problem that few seem to be facing up to.

I read somewhere that in the event of a total failure of one signalling centre, others will be able to take control of bits of its area. Part of me prefers the idea of bits of wood bolted to posts and tied to a lever in a box with a man who waves with a cheerful smile... or not...

I think you are fundamentally correct in saying the above.

With regards to smaller, more local signal boxes, I think they should remain, with all complying with a single secure protocol and able to be overridden by a control centre, and, indeed, vice versa, where a failure occurs. The notions of a lack of backup and any multiple incompatible protocols are a recipe for slight or total chaos in situations where problems occur.
 

tirphil

Member
Joined
27 Jan 2011
Messages
275
Location
Wales
Won't HS2 be moving block using ETCS Level 3 so the computers run the whole show?

ERTMS level 3 has not been developed yet although the intention is that level 3 should be moving block. To do this the trains will need determine and report their own location to the signalling control centre via GSM-R radio. The control centre will then determine track section occupancy from position reports received from trains and will transmit movement authorities to trains via the GSM-R.
 

Nym

Established Member
Joined
2 Mar 2007
Messages
9,785
Location
Somewhere, not in London
Won't HS2 be moving block using ETCS Level 3 so the computers run the whole show?

Quite asside from the fact there is no true 'moving block' signalling system... Yes, ETCS 3 should work on very small blocks with permissable speeds calculated using an extremely complicated algorythm taking into account vehicle performance, other vehicles' performance, points, linespeeds, speeds, etc etc.

But the gains over standard block signalling when you're using homogenous performance stock with well planned stopping patterns could be argued to be marginal, with the only real performance increase being headway reduction, proberbly down to approximately 2 to 3mins, but then you're into the realm of being limited by points interlocking performance and linespeeds at points, you'll tend to have a fluid movment with a small delta algorythm and services will start bunching up near to points, where headways increase, and if you want to get into the real technicallities of fluid dynamics and traffic movment, you then start looking into how much the algorythm considers, if it only takes into account near units like TCAS then you can have the tendancy to have oscilations of slow patches moving down the line from pinch points, giving very unpredictable performance. However, if it's a whole system algorythm, (Very big, and very complicated!) then it would be perfect, but the processing time would be too long. A nice halway house could be worked by the addition of a 'bunching factor' allowing taking into account traffic up to say, 5 or 6 assignments infront to prevent bunching.

To test this though I'd have to start looking at writing and modelling algorythms... If I end up working at ARUP and I'm being paid mega money to do this, yeah, fine, for the benifit of a railways forum, nah.

Either way, TVM430 'Moving Block' that isn't really moving block, it's fixed block target speed signalling, allows up to 16 or 18tph depending on linespeeds.

For HS2 I would be expecting headways to be dominated by points, and therefore, with the station layouts that would be needed for layover times, I'm reconing on an upper limit in the core section of about 22 - 24tph, 2min headway for points changeover etc, and some very clever timetabling for points bunching etc, and fastchange points, I'm talking <10secs to interlock. So that the points headway is added onto the stopping headway (how long it would take to emergency stop the unit) so you can push it down to 2mins, possibly, But 3mins and 18tph is much more realistic, although I would recon you might be able to emergency stop from 220mph in 1min20secs it wouldn't be comfortable, so couldn't be relied upon for operational use. 20tph would be what I'd be targeting, since thats pushing the limits of what 10 platforms at Euston could take, an extra 6tph on the fast core could come from Heathrow and HS1 services, but without homogenous stock, everything either slows down or you loose capacity. Hence why I'd be after 4track between OOC and Birmingham Delta, 3mins headways would still allow up to 34 - 36tph on the core section, and allow for a 'stopper' calling in the chilterns.
Euston would max out at 24tph, but running slower = only need 2 track for 24tph between OOC and Euston, with some tph going onwards to Heathrow and some tph going onwards to HS1 the extra 6tph can take you up to 30tph, loosing 6tph paths for the slower services, or for non-homogenous stock to run on the HS2 lines between OOC and Birmingham Delta with less issues, such as DBS or SNCF stock running on HS2 wouldn't be the same as the HS2CC or HS2CA stock.
 

68000

Member
Joined
27 Jan 2008
Messages
832
I believe that hacking will become a much bigger problem generally over the coming years.

I do believe that the railway is/will be exposed to some risk. It may all be failsafe, and so the worst that can be done is to stop trains but if that happened for an extended period of time it would cause problems. Lets face it, if people are stuck on a train for an hour they get angry, and for any more than that they start breaking out.

With signallers controling greater areas the ability to talk drivers past signals is reduced so whatever the cause of signal failures, it is a problem that few seem to be facing up to.

I read somewhere that in the event of a total failure of one signalling centre, others will be able to take control of bits of its area. Part of me prefers the idea of bits of wood bolted to posts and tied to a lever in a box with a man who waves with a cheerful smile... or not...

You may prefer it but is costs an awful lot of money to have thousands of local control areas
 

Tracky

Member
Joined
18 Jul 2011
Messages
483
You may prefer it but is costs an awful lot of money to have thousands of local control areas

Part of me prefers the idea - as I say. What I would like to happen before the new ways come in is a clear recovery plan for getting trains moving well within an hour when things go wrong...
 

Jonny

Established Member
Joined
10 Feb 2011
Messages
2,577
The worst case scenario might well be an attack where all the points get locked in one configuration - that could still mean chaos and overcrowding around some major terminals though if nothing can enter or leave.
 
Status
Not open for further replies.

Top